A flaw discovered by artificial intelligence in the PHP programming language has triggered a wave of shutdowns of various websites and government servers across the world.
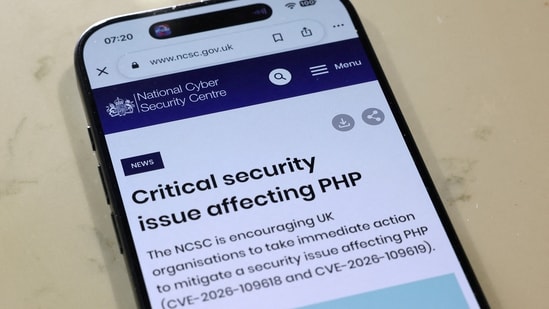
On Wednesday, cybersecurity experts discovered a pair of vulnerabilities, dubbed PHP2Shell, with the help of AI models.
What is PHP?
PHP, which is a recursive acronym for PHP: Hypertext Preprocessor, is a free, open-source, server-side scripting language designed specifically for web development. This programme serves as the invisible engine behind a website.
Deep Dive
What are the two PHP security vulnerabilities?
How were the PHP vulnerabilities discovered?
Should website owners update PHP or take their sites offline?
Created in 1995 and initially called 'Personal Home Page', PHP is known as the the server-side language and is responsible for assembling content and delivering pure HTML code to the respective browsers.
PHP is commonly used for content management systems, major tech platforms such as social media websites, and e-commerce applications.
Also Read | Weak web IDs and a decade-old PHP flaw. The week the internet's plumbing showed its cracks
AI models and research flag serious security flaws
Researchers at security firm Calif, working with OpenAI, reported the first flaw on August 11.
{{/usCountry}}Researchers at security firm Calif, working with OpenAI, reported the first flaw on August 11.
{{/usCountry}}"Given the severity of these flaws and PHP’s widespread use, we consider this one of the most impactful security issues in recent memory," said OpenAI in a statement.
According to Alphabet-owned security firm Wiz, the PHP language powers around 70 percent of the websites in the world.
It is also the programming language powering WordPress, Joomla, Drupal, Wikipedia’s MediaWiki, and many others on the internet. The flaw by Wiz was first reported on August 24.
With world leaders shutting down websites amid the panic, here's a look at the latest developments -
PHP security vulnerabilities | Top updates
- Govt websites taken offline across the world: Authorities in Europe, Asia and other continents have temporarily taken certain government websites offline to protect against newly discovered security vulnerabilities. The concerns also resulted in a rare public warning from the United States National Security Agency (NSA), UK's National Cyber Security Centre, and CERT-EU
- 'Most severe flaws ever seen': In a statement addressing the vulnerabilities, nonprofit group PHP Foundation said on Wednesday that the flaws were among the most severe it had encountered. The group also called on website administrators to update their code immediately.
- Vulnerability 1 - CVE-2026-109618: As per the PHP foundation, CVE-2026-109618, or Remote Code Execution (RCE) via OOM corruption, is among the two critical remote code executive vulnerabilities found. This issue can result in the PHP leaving partially initialised internal data behind and later treating it as valid, corrupting memory.
- Vulnerability 2 - CVE-2026-109619: The other error is CVE-2026-109619 or RCE via stale global state. As per the non-profit group, a fatal error at the wrong point in the PHP could leave internal state pointing to memory that belonged to a previous request. Both of these vulnerabilities have a score of 9.2 on the Common Vulnerability Scoring System (CVSS).