
 E-Paper


Cyberattack targets refrigerators at French supermarkets: Why nothing is un-hackable
Hundreds of French supermarkets suffered refrigeration disruptions in a cyberattack, with some forced to discard food.

 Prefer HTon Google


A cyberattack knocked out fridges and freezers at about 700 of France's 10,000 supermarkets, French finance minister Roland Lescure told Parliament on Tuesday. Some stores had to bin food. Danfoss, the Danish company that supplied the refrigeration management software, said most of the affected systems were older products that no longer received software or security updates.
Machines that are left running on code no longer monitored or patched are one reason security specialists treat almost every connected device as hackable. Anything with a chip and a network connection runs code, all code has bugs, and an attacker with enough time and money will find one.
What happened
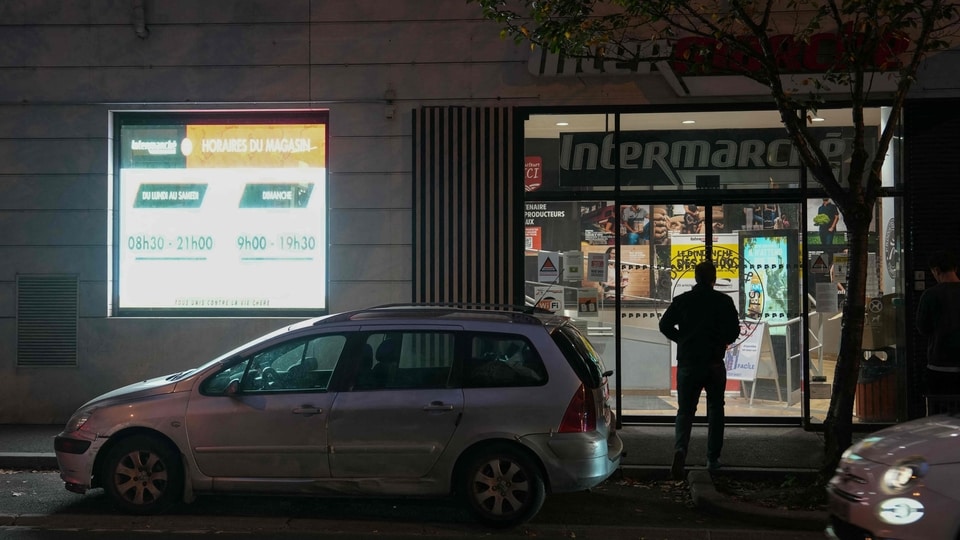
The attack hit refrigeration management systems, the computers that coordinate the controllers coordinating a supermarket's chillers and freezers functioning. Groupement Mousquetaires, which runs more than 4,000 stores across Europe, said 300 of its Intermarché and Netto stores were affected, with some refrigerated and frozen display cases still out of service on Tuesday. Dominique Schelcher, chief executive of the French chain Coopérative U, said 80 of its 2,000 stores were hit; most kept the cold running, but some had to throw food away. Carrefour and Monoprix stores were also affected.
Lescure said France's food supplies were not at risk, but that the attack "touches the heart of our food security". The Paris prosecutor's cybercrime unit is investigating, including the damage from spoiled food and reports of fires. The attackers or their methods are yet to be determined.
Danfoss said it "has long advised customers to keep supported systems updated with the latest firmware, as well as to operate behind a firewall." By its own account, most of the machines that failed had fallen out of support.
When the patches stop
Every program ships with bugs, and some of them let an outsider make a machine do things its owner never intended. When a maker finds one, it releases a fix, called a patch. That is why our phones (and most digital devices – such as smart speakers) get updates. Trouble starts when the owner never installs the patch, or when the maker stops writing them because the product has reached the end of its life. A chiller can keep humming for years with undetected (or even detected, but unpatched) code flaws.
Such machines are easy to find, too. When researchers at Claroty, an industrial cybersecurity firm, searched an internet-scanning service for one current Danfoss refrigeration manager, the AK-SM 800A, they found 2,765 reachable from the public internet, many showing their web control panel. That model has not been linked to the French attack, but the count shows how exposed this class of kit is. When rival chains buy from the same supplier, one ageing product line can leave all of them open at once.
Exploits, code written to abuse a bug, were the commonest way into the networks that Mandiant, Google's incident-response unit, investigated in 2025, at 32% of intrusions, the sixth year running they topped its list.
Bugs nobody knows about
The most sophisticated cyberattack uses a bug the maker does not know exists. That is a zero-day, so called because the maker has had zero days to fix it. It was this sort of a bug that NSO Group, the now-bankrupt Israeli firm that made the powerful Pegasus spyware, used. Google's Threat Intelligence Group counted 90 zero-days exploited in 2025, up from 78 in 2024 and short of the record 100 in 2023. Nearly half (43) hit business software and equipment, and about half of those were in security and networking products, the gear meant to keep attackers out.
For the first time, Google tied more zero-day attacks to commercial spyware vendors, companies that sell surveillance tools, typically to governments, than to traditional state espionage groups. It linked at least 10 to groups it assesses as China-linked espionage actors and nine to financially motivated gangs, two of them in attacks that ended in ransomware, malicious code that locks up a victim's systems until a ransom is paid. A zero-day loses its value once the maker patches it, so attackers tend to save them for targets worth the spend.
Mandiant says "exploitation is routinely occurring before a patch is even released", and estimates that attacks now come, on average, about a week ahead of the fix.
Small bugs, stacked
Claroty also found three bugs in the AK-SM 800A. One let an outsider skip the login screen. Another let a logged-in user slip commands into the alarm-email settings and have the machine run them, and a third let a logged-in user knock the web interface offline. The second bug needs a password an attacker should not have; pair it with the first and the password stops mattering. Security researchers call this chaining, and Claroty said its findings "create powerful attack chains against internet-accessible cyber-physical systems", meaning computers that run physical machinery. Danfoss published patches in 2025, and there is no evidence yet that these bugs were linked to the French attack.
Who attacks, and who gets hit
Attackers want different things. States want intelligence and footholds in other countries' infrastructure, spyware vendors want access to sell, gangs want ransom money, and hacktivists, activists who hack, want attention.
Some victims are picked. Many more simply turn up in a scan, since a machine on the open internet running code with a known bug is a target whatever anyone thinks of its owner. Food retailers, hospitals and power suppliers make tempting marks because every hour offline costs them, which raises the pressure to pay.
The criminals have also specialised. Mandiant found that in 2025, the median gap between one group breaking into a network and handing access to a second was 22 seconds, down from more than eight hours in 2022. In ransomware cases, the commonest way in was access left behind by an earlier intruder, at 30%.
What AI changes
AI makes every one of these routes cheaper. Google's threat team expects attackers to "utilise AI to automate and scale attacks by accelerating reconnaissance, vulnerability discovery, and exploit development", which means finding exposed machines, finding new bugs and writing the exploits.
In November 2025, Anthropic, the company that makes the Claude AI models, said it had disrupted a campaign it assessed "with high confidence" was run by a Chinese state-sponsored group. The attackers manipulated its Claude Code tool into attempting break-ins at about 30 organisations worldwide, succeeding in a small number; Anthropic said AI performed 80-90% of the campaign. They slipped past its safeguards by breaking the job into small, innocent-looking tasks and posing as a legitimate security firm. The model also fumbled, at times inventing login credentials or passing off public information as secret.
Anthropic caught that misuse because it ran the model. Open-weight models, which anyone can download and run on their own machines, have no supervision. In 2024, researchers showed that in 13 open chat models, the tendency to refuse harmful requests runs along a single internal direction, and that deleting it stops the refusals. The technique has become known as abliteration, and an abliterated model has no guardrails left to trick. For now abliterated models are an emerging risk, with thin public evidence of their use in real attacks.
Defenders have the same tools. In 2024, Google's Big Sleep AI agent caught an exploitable bug in SQLite, a widely used database, before the code shipped.
What helps
Danfoss's guidance tells operators to protect its devices from "direct internet exposure", change default passwords at installation and keep software "fully updated". Kit that can no longer be patched needs replacing or cutting off from outside networks, and a store's network can be split so that a break-in at the fridges never reaches the tills. From December 2027, the EU's Cyber Resilience Act will require manufacturers to handle security flaws across their products' lifetimes.


